
Encryption managed by Notabene
Guide on PII encryption and submission using Notabene SafeTransact, including endpoint usage, PII re-use conditions, and response handling.
For Notabene SafeTransact-managed PII Encryption and Submission
- Endpoint to use:
{{url}}/entity/:entityDID/tx/:tx/append - Use Case: Submit PII to be encrypted and stored locally on Notabene’s platform.
- Encryption Process: Notabene encrypts data with your Entity's keys to prevent unauthorized access.
- Data processing: Notabene re-encrypts your data (PII) and sends it to requesting counterparties if and where applicable and not blocked.
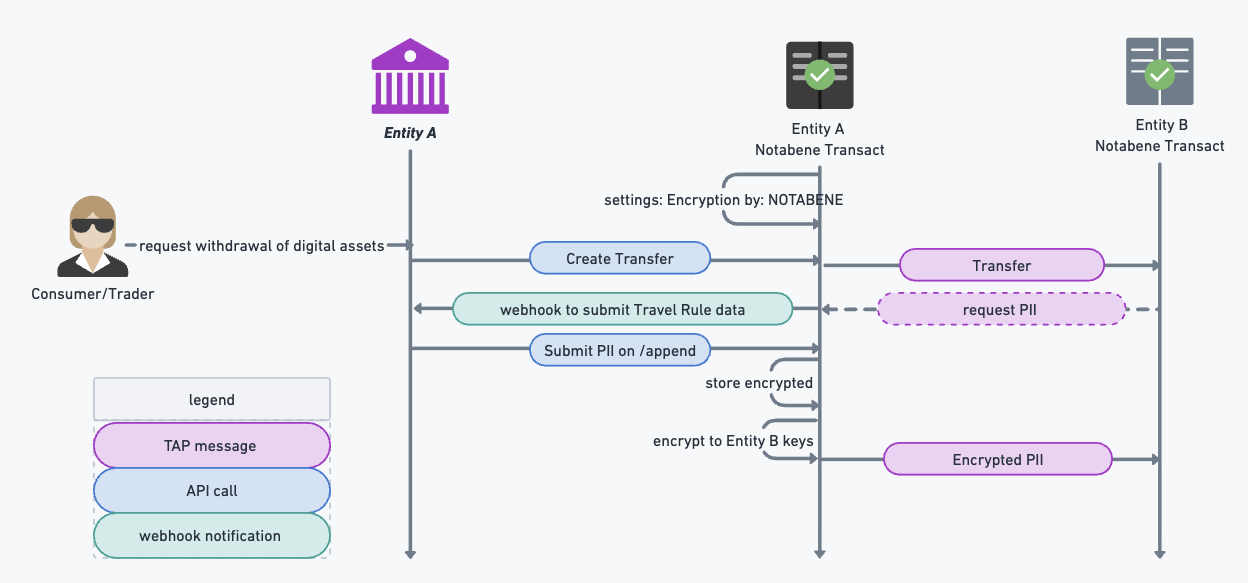
PII Re-use Conditions:
- PII can be reused if
txAppendis called with both originator and beneficiary@id. - Reuse is only for PII you created; received PII is not reused.
- Update reusable PII by calling
txAppendagain with new data. -
{
  originator: {
    "@id": originatorIdentifier,
  },
  beneficiary: {
    "@id": beneficiaryIdentifier,
  }, //these are optional and set re-use to TRUE.
    "ivms101": {
        "originator": { /etc.
Payload Requirements:
- Include only necessary fields in IVMS format.
- Optional: Reference originator and beneficiary
@idfor reuse eligibility.
Validation:
- Transfer ID must exist.
- Transfer must be of type Travel Rule (
"isTravelRule":"true"). - IVMS content is validated against local jurisdiction rules when your transfer is of type Travel Rule, otherwise validation is skipped.
Responses:
- Success (202):
{ "message": "Transfer appended successfully with encrypted PII" } - Error (400):
{
  "error": "Invalid IVMS101 data",
  "details": {
    "errors": [
      "Missing required fields for the definition https://pd.notabene.id/ivms101/v1/JP-0.json"
    ],
    "missingFields": [
      "$.originator.originatorPersons[0].naturalPerson.name.nameIdentifier[0].primaryIdentifier"
    ]
  }
}
PII Blocking Conditions:
- Transfer is flagged.
- Waiting for counterparty confirmation of wallet/beneficiary ownership
- Counterparty rejected or cancelled.
These conditions also apply to PII reuse.
Updated 9 months ago
What’s Next
Did this page help you?